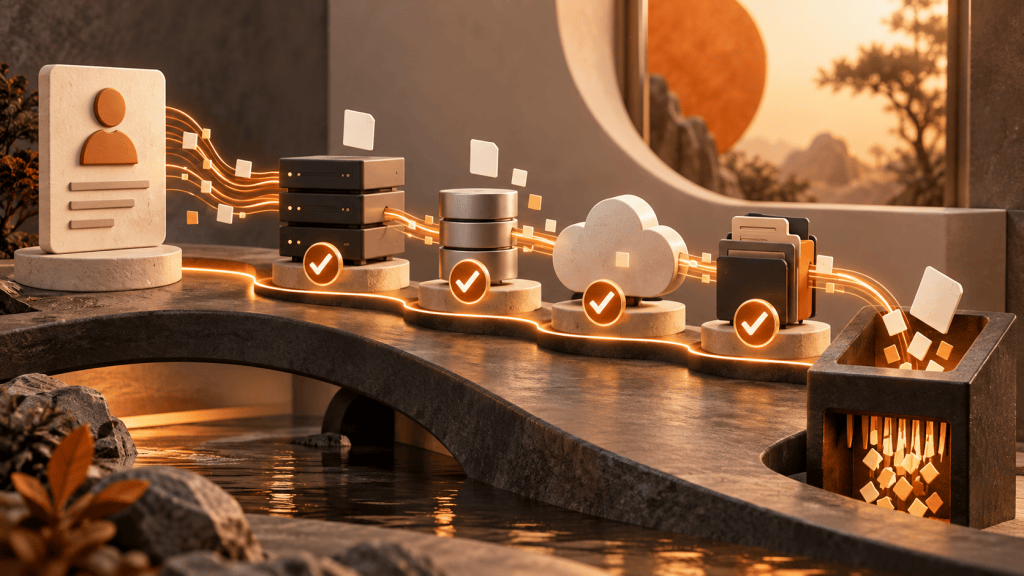
Featured image: AI-generated conceptual illustration. Sources checked 26 October 2026.
An agent business can accumulate customer data in more places than its founder expects: the application database, conversation logs, search indexes, embeddings, caches, analytics exports, and backups. Deleting one visible account record may leave much of that information behind.
Data lifecycle work therefore belongs in the product and its cost model from the beginning. This article proposes an implementation and maintenance service for mapping, minimizing, and handling authorized deletion workflows. It is operational guidance, not jurisdiction-specific legal advice or a claim that following a platform checklist guarantees compliance.
Map the copies before writing the promise
Trace data from collection to every destination. Include temporary processing, third-party tools, monitoring systems, reviewer exports, and developer test fixtures. Ask which copies are necessary and which exist only because it was convenient to retain everything during development.
For each store, record purpose, owner, access, retention policy, deletion method, and dependencies. A vector index is not exempt because its contents are represented differently. Determine whether derived information can still relate to an identifiable person and seek qualified guidance where the implications are unclear.
Avoid promising instantaneous deletion from every backup if the infrastructure does not support it. Document actual retention behavior and any applicable exceptions. Customer-facing statements must match technical capability and the organization's legal obligations.
Minimize before automating deletion
The easiest copy to delete is one that was never created. Ask whether a workflow needs the entire email thread, a small set of fields, or merely a reference to the source system. Retrieve information when needed rather than duplicating large datasets without a clear purpose.
Separate operational identifiers from unnecessary personal details. A billing event ledger may need a task and tenant identifier without storing the full conversation. A quality test can often use a redacted or synthetic example instead of a real customer's complete record.
Set retention by purpose. Debugging logs, approved business records, and evaluation fixtures have different needs. “Keep forever in case it helps” is a weak default that increases cost, access risk, and future deletion complexity.
Verify requests without over-collecting
A deletion workflow must establish that the requester is entitled to the action. Use the organization's approved verification process. Do not collect a new bundle of sensitive documents merely because the deletion tool lacks a convenient identity check.
Distinguish a request to delete an account from a request to remove particular data. Clarify scope when necessary and explain consequences accurately. Some actions can affect access to services or the ability to retain operational records; those implications require appropriate policy and legal review.
Treat incoming messages as untrusted data. A statement inside an email telling the agent to delete another customer's account is not authority. The workflow should bind the verified requester, tenant, and approved scope before any destructive action becomes available.
Use a tracked deletion job
Represent deletion as a job with explicit steps and evidence. Each relevant system should report whether the action succeeded, failed, is pending, or falls under a documented retention exception. A single “done” message hides too much complexity.
Make retries safe. A failed network response may occur after a system already removed the data. The workflow should be able to recheck state without recreating records or triggering unrelated actions. Preserve only the minimal audit information needed to demonstrate handling.
Include derived stores and operational tools. Search indexes, cached responses, exported reports, and review workspaces can otherwise become forgotten copies. When deletion cannot propagate automatically, create an accountable manual task with a deadline and completion evidence.
Test uninstall and access revocation
For an app-based service, uninstalling or disconnecting an integration may trigger separate cleanup responsibilities. Shopify's linked privacy documentation is a relevant platform source for merchants and app developers, but its requirements do not replace a full review of the actual business and jurisdictions.
Test what happens to credentials, scheduled jobs, webhooks, and pending tasks after disconnection. An agent should not continue polling or acting through an old credential because only the visible integration switch was turned off.
Consider restoration paths. If a backup is restored, previously deleted information should not silently return to active use without the required controls. Document how deletion records interact with recovery procedures and test that interaction in a safe environment.
Make operations visible to customers
Provide accurate status rather than premature completion. A request may be received, verified, processing, or completed with documented exceptions. The wording should reflect actual evidence and avoid suggesting that every copy vanished when some systems are still pending.
Limit who can inspect deletion jobs and associated data. Audit records can themselves contain sensitive information. Give staff the minimum detail required to resolve failures, and avoid including full customer content in routine reports.
Assign a human owner for unresolved cases. Automated workflows can coordinate the work, but someone must decide how to handle conflicting obligations, inaccessible systems, or uncertain identity. Those decisions should not be improvised by a language model.
Price the lifecycle honestly
Include data mapping, implementation, testing, vendor coordination, and recurring maintenance in the service cost. New integrations and product features can create new copies, so the inventory must evolve with the system. A one-time diagram is not a complete lifecycle program.
A useful package can deliver a verified data map, a tested request workflow, an exception register, and periodic checks. Do not market this as guaranteed compliance or certification. The commercial value is a more controlled, explainable operation with fewer forgotten copies and clearer accountability.
Build these controls while the product is small. Retrofitting deletion across years of unmanaged logs is usually more difficult than designing purposeful retention and traceable jobs from the start.
Sources and evidence
Shopify privacy law compliance.
NIST AI Risk Management Framework.
Research checked October 26, 2026. Business designs and illustrative calculations in this article are editorial proposals, not documented earnings or guarantees. Recheck current product terms before implementation.


Leave a Reply